<img height="1" width="1" style="display:none;" alt="" src="https://px.ads.linkedin.com/collect/?pid=7178634&amp;fmt=gif">
uControl Book a demo
uControl TekTrust

Trust your CMDB. Prove it.

Don’t just trust it — TekTrust it. TekTrust is a verifiable trust layer between what discovery finds and what your CMDB records. It continuously validates your ServiceNow CMDB against BMC Discovery — turning CMDB accuracy from something you believe into something you can evidence.

  • Continuous CMDB validation — every sync becomes a checkpoint
  • Board-level RAG status, engineer-level evidence to act on
  • Read-only — never writes back to your CMDB
CI by CI
BMC Discovery ↔ ServiceNow
4 classes
of defect caught continuously
Read-only
zero writes to your CMDB
Board + engineer
one view for each
The problem

Your CMDB runs the business. But who checks the CMDB?

Change management, incident response, service mapping, audit — every one of them trusts the CMDB is right. Yet with multiple sources feeding it, discrepancies build up that are almost impossible to see from inside the CMDB itself.

It can look complete while quietly carrying errors that surface at the worst possible moment: a failed change, a missed dependency in an incident, an audit finding.

Trust shouldn’t be assumed. It should be proven.

What TekTrust catches

Four kinds of CMDB defect. Caught before they cost you.

TekTrust compares what BMC Discovery sees against what ServiceNow records, and surfaces exactly where they disagree.

Missing CIs

Infrastructure Discovery found that never made it into the CMDB — the assets you’re managing blind.

Attribute drift

Field-level disagreements between what was discovered and what’s recorded — so the CMDB reflects reality, not a stale snapshot.

Over-merged records (duplicates)

Multiple real devices collapsed into a single CI — hiding scope, risk and licence exposure.

Missing relationships

Dependencies Discovery identified that the CMDB doesn’t hold — the connections your service models and impact analysis rely on.

See it in action

From red/amber/green to the exact record.

At a glance

One status across every pairing.

A single overview shows estate data-quality status and every configured pairing — CI health, attribute issues, relationship health and over-merges — so you always know where the CMDB stands.
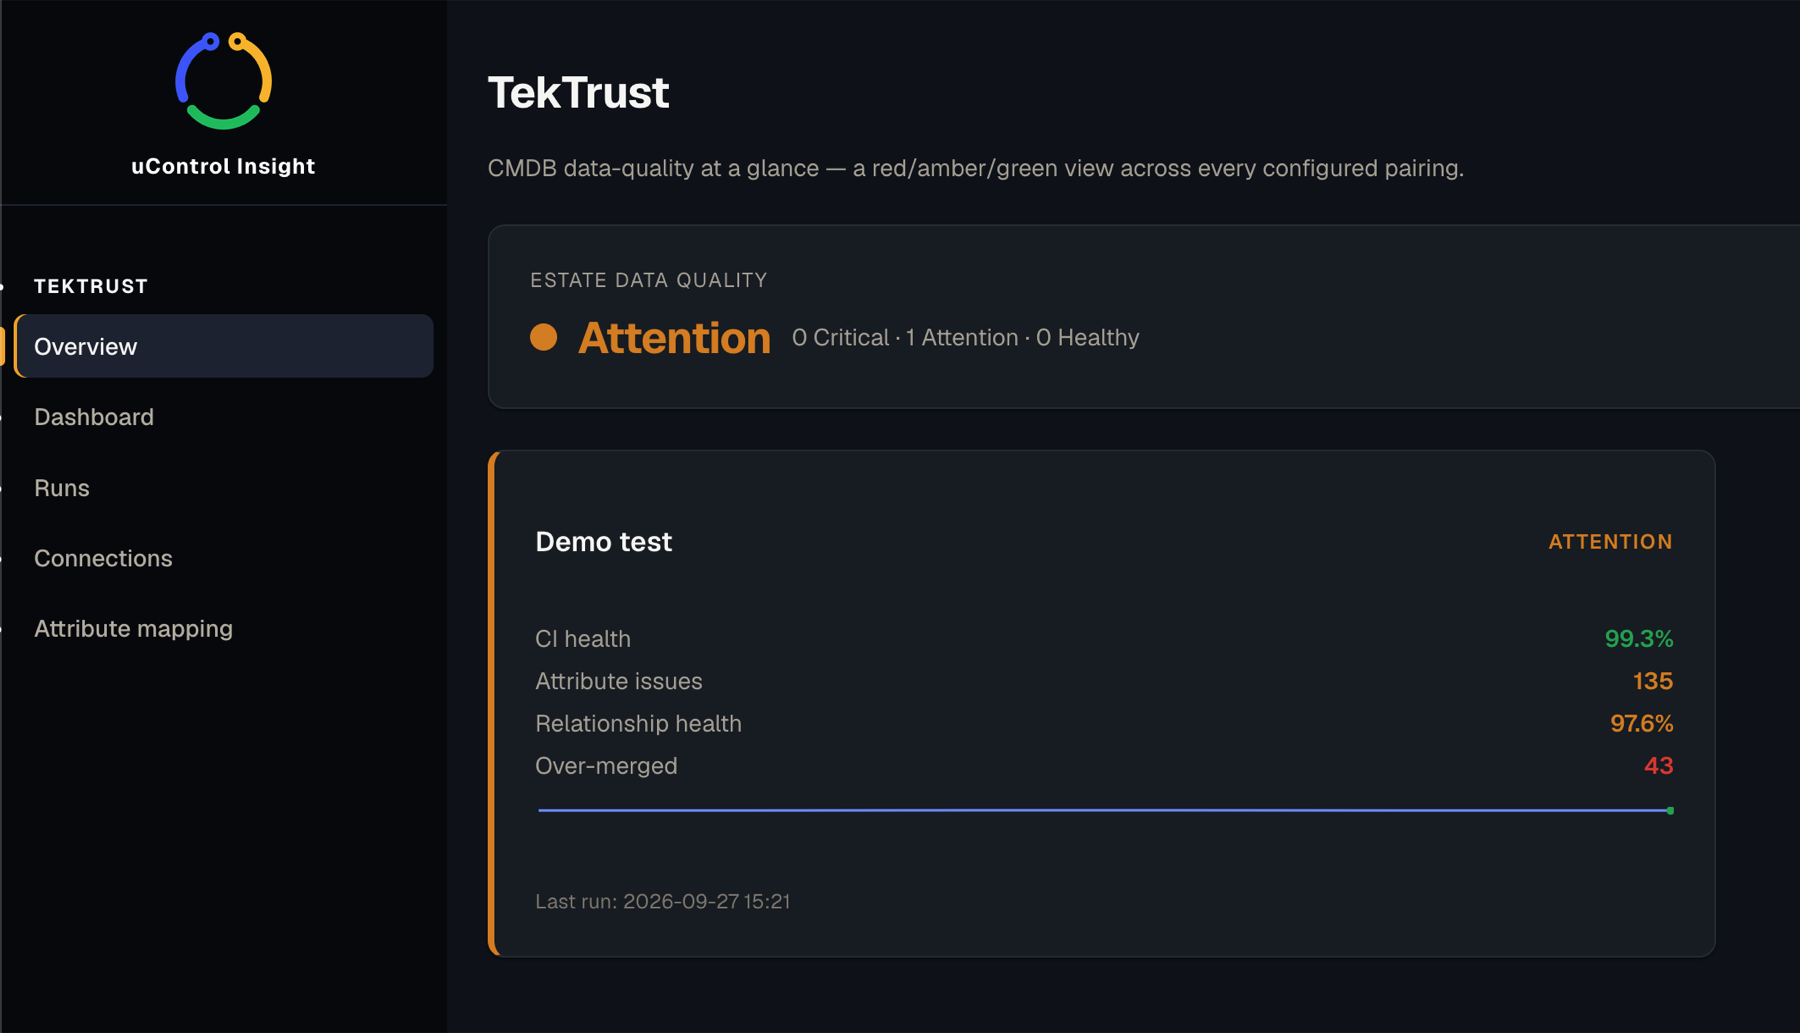
  • Red / amber / green across the whole estate
  • Every configured Discovery ↔ ServiceNow pairing
TekTrust overview — estate data-quality status across every pairing
Down to the evidence

Every finding, with the proof attached.

Drill from any red or amber score straight into the exact CIs, attributes and relationships that disagree — expected versus actual, ready to hand to an engineer.
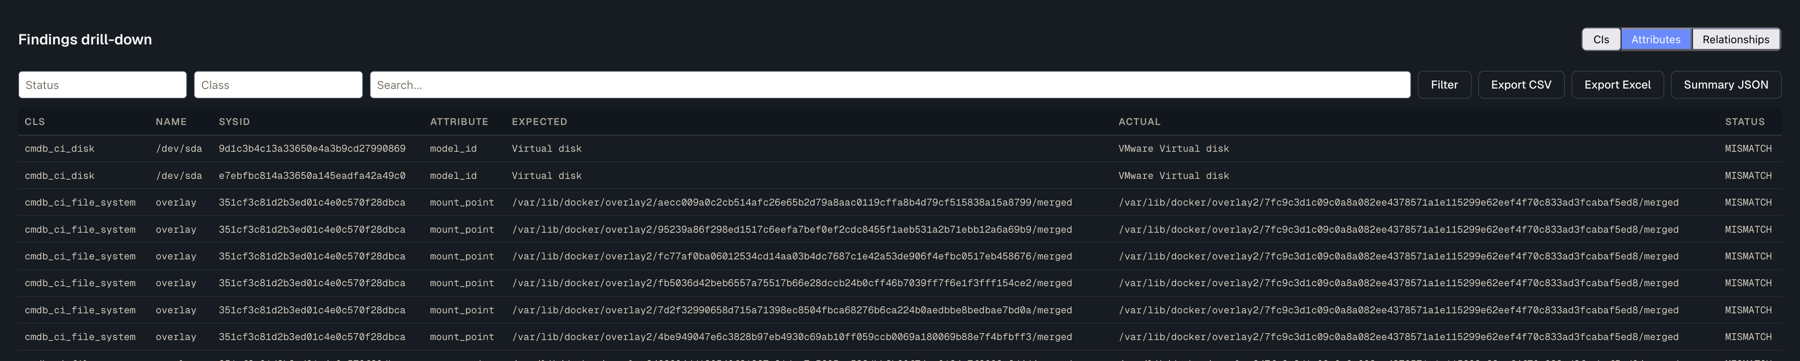
  • Expected vs actual, per attribute
  • Export to CSV, Excel or summary JSON
TekTrust findings drill-down — expected versus actual attribute values
Built for two audiences

Status the board understands. Detail engineers can action.

A single RAG dashboard gives leadership a clear, defensible view of CMDB health and trend over time. Underneath it, every red and amber drills straight down to the specific CIs, attributes and relationships an engineer can investigate and fix.

One tool, both conversations — no exports, no spreadsheets, no arguing over whose data is right.

See how TekTrust creates a verifiable trust layer for the CMDB.

DiscoverCompareValidateEvidenceInvestigateAct
Scenarios

When the CMDB is wrong, the business feels it.

Three places CMDB accuracy quietly decides the outcome — and what changes when it’s proven.

Scenario A

The change that shouldn’t have failed

A “low-risk” change goes ahead and takes down a service nobody flagged as connected.
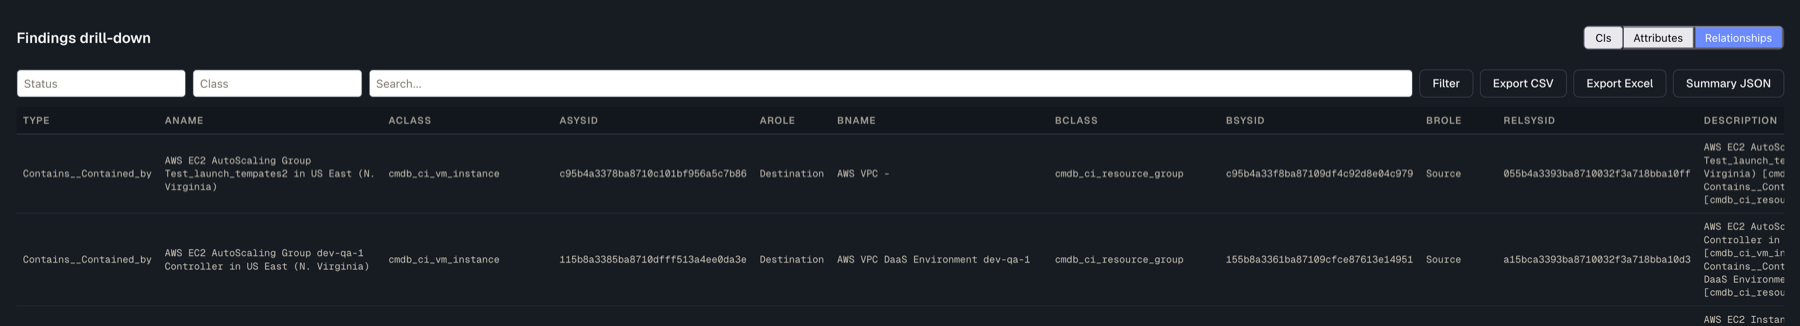
  • With TekTrust — the missing dependency was surfaced weeks earlier. Discovery had seen the relationship; the CMDB never held it.
  • The outcome — change decisions built on dependencies that actually exist. Fewer failed changes, fewer surprises in the CAB.
Scenario A — a change fails on a dependency the CMDB never held
Scenario B

“Prove the CMDB is accurate”

An auditor — or the board — asks how you know your CMDB is right. The honest answer is a shrug and a spreadsheet.
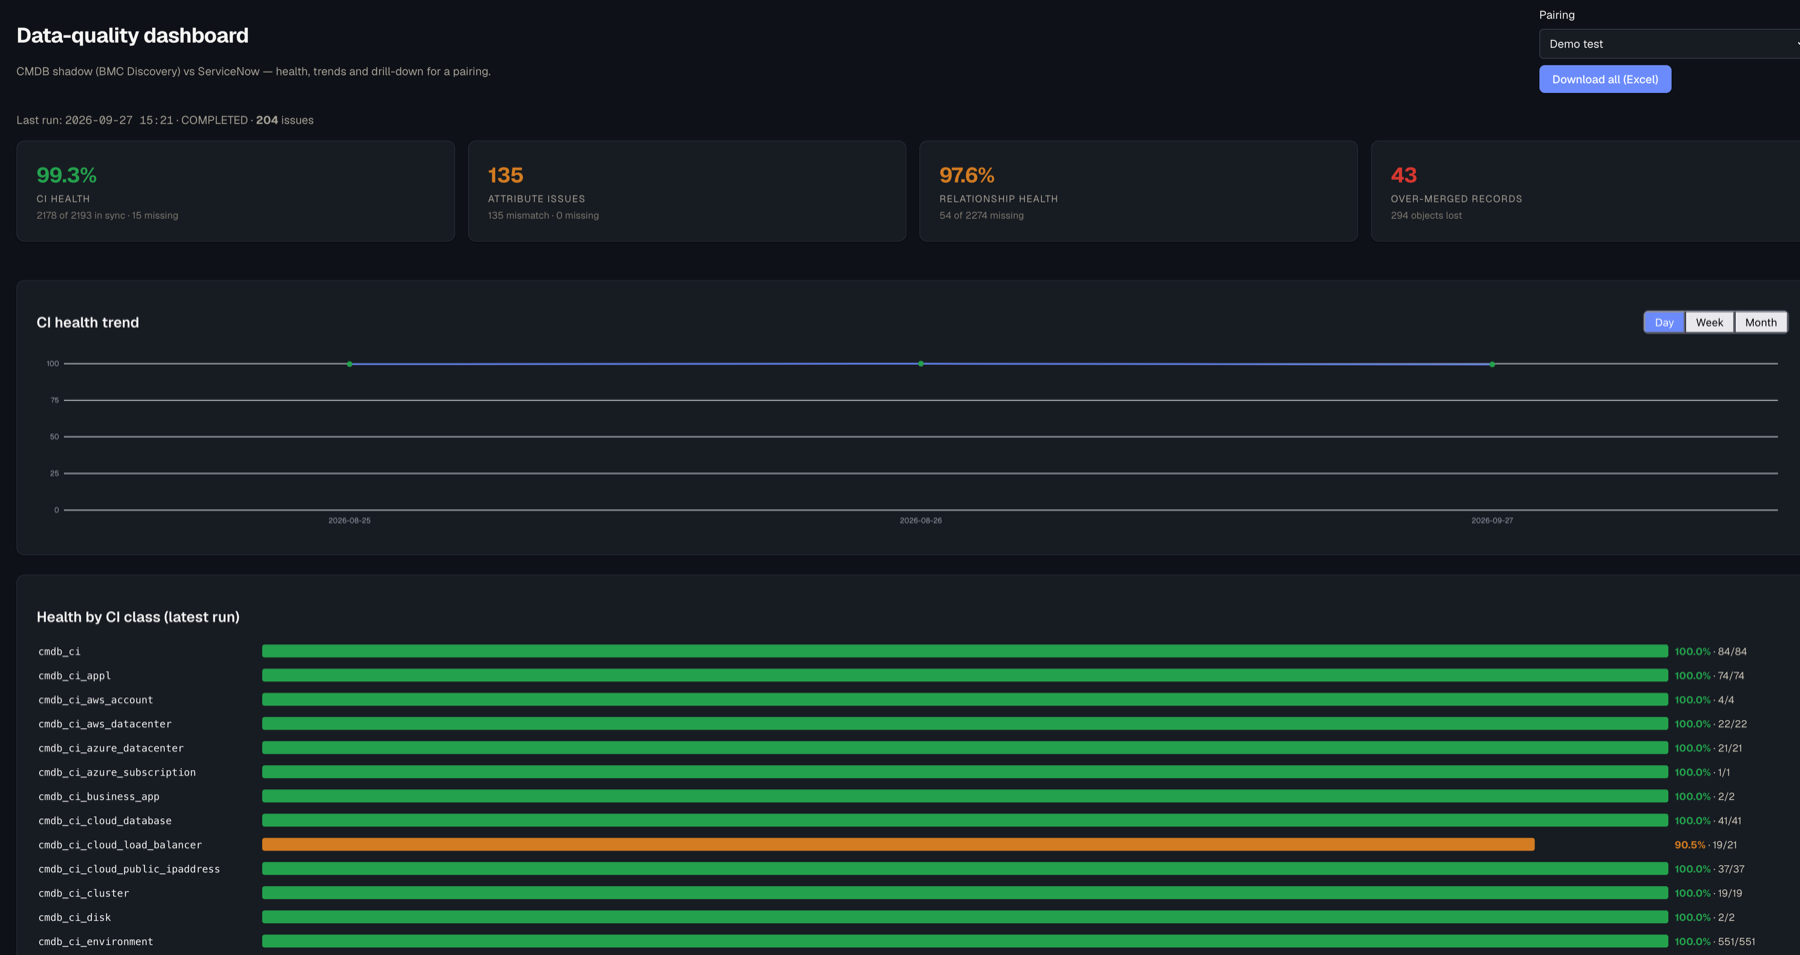
  • With TekTrust — a dated RAG dashboard shows CMDB health and its trend over time, with the evidence behind every score.
  • The outcome — governance and audit backed by proof, not belief, and a trend line that shows it improving.
Scenario B — a dated RAG dashboard evidences CMDB accuracy and its trend
Scenario C

The devices hiding inside one record

Licence and risk reporting look healthy — because several real devices are collapsed into a single CI, masking the true count.
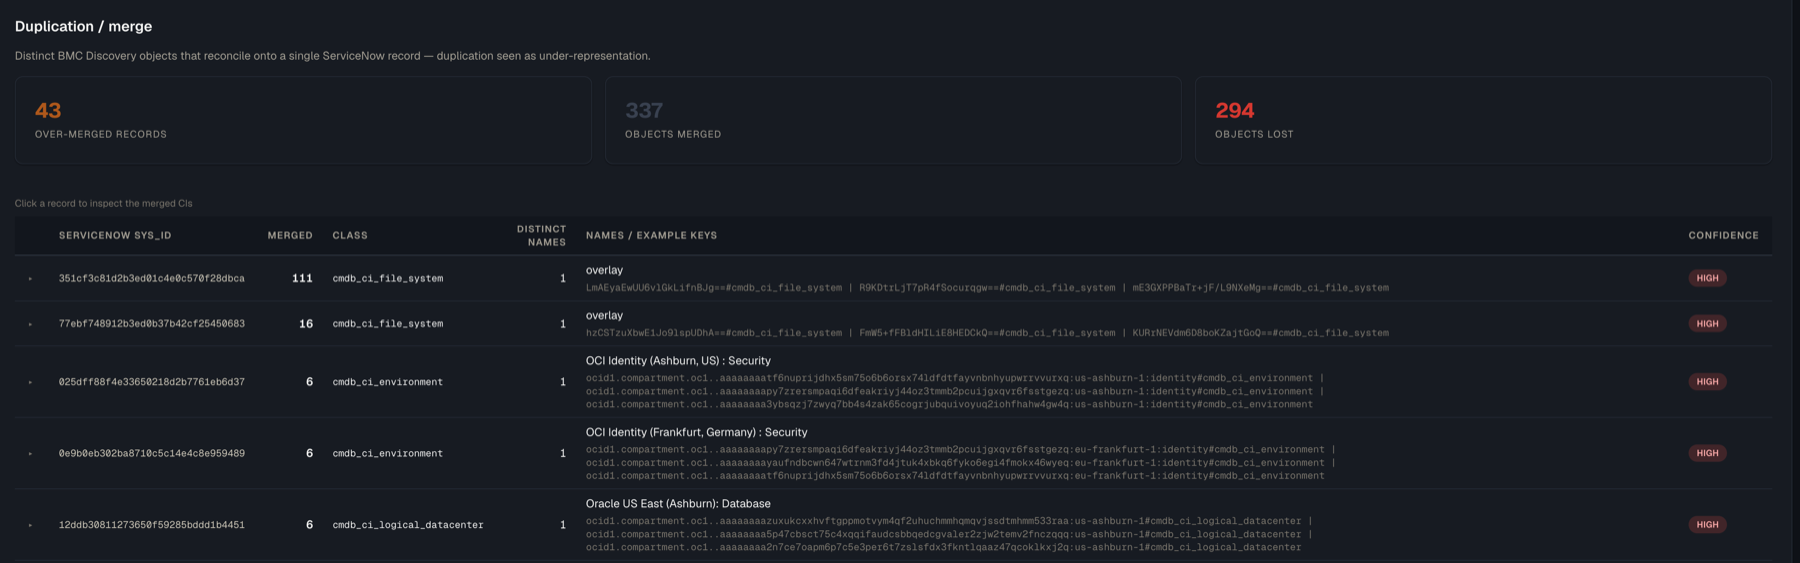
  • With TekTrust — over-merged records are surfaced as candidates to review, with the evidence attached.
  • The outcome — true scope restored: accurate licence exposure, risk posture and asset counts.
Scenario C — over-merged records surfaced to restore true device scope
Where it fits

Independent by design. Secure by default.

TekTrust sits between your discovery and your CMDB as an independent checkpoint — so your assurance never depends on the systems it’s checking. It reads; it never writes back.

Read-only validationNever writes to your CMDBAES-256-GCM encrypted credentialsRBAC + full audit logSSO · SAML · OIDC · LDAPDeploy anywhere — on-prem · cloud · hybridKeeps data in your network (on-prem collection)
Questions

Frequently asked.

Does TekTrust change anything in our CMDB?

No. It’s strictly read-only and one-directional — it validates and evidences, and never writes back to ServiceNow or BMC.

We have 20+ sources feeding our CMDB — is that a problem?

No. TekTrust focuses on assuring that what BMC Discovery contributes lands correctly; records owned by your other sources are out of scope, so you get signal, not noise.

Can this run inside our own environment?

Yes — on-prem, cloud or hybrid, with an on-prem collection option that keeps sensitive CMDB data inside your network.

Is it just a report, or something we can act on?

Both. Board-level RAG for status and trend, and per-finding detail engineers can investigate immediately.

How secure is the data?

Credentials are encrypted at rest (AES-256-GCM), access is RBAC-controlled with a full audit log, and SSO is supported via SAML, OIDC and LDAP.

Why we built it
A CMDB only earns trust when that trust can be proven. We built TekTrust to make CMDB accuracy continuous and evidence-backed — so leadership gets a status they can stand behind, and engineers get the exact detail to put it right.
S Steve Hicks CTO, TekWurx

Stop believing your CMDB. Start proving it.

Book a demo and we’ll validate a live CMDB against discovery in a single session — and show you exactly where the gaps are.

Book a demo